
Login Audit
Package docs status
Section titled “Package docs status”This page is generated from package source documentation in the Capell packages repository and the checked-in manifest. Source documentation is not distribution status. Before running a Composer command, verify that the exact package and compatible 1.x release are available through public Packagist or the authenticated marketplace account.
| Field | Value |
|---|---|
| Composer package | capell-app/login-audit |
| Package slug | login-audit |
| Product group | Capell Security & Compliance |
| Tier | premium |
| Bundle | security-compliance |
| Runtime contexts | admin |
| Capell version | ^1.0 |
| Catalogue role | extension |
| Release channel | Beta |
| Source repository | capell-app/packages |
| Source path | packages/login-audit |
| Docs source | packages/login-audit/docs |
| Manifest | capell.json |
What This Plugin Adds
Section titled “What This Plugin Adds”Login Audit is an Available, Schema-owning Capell package in the Capell Security & Compliance product group. It ships as capell-app/login-audit and extends these surfaces: admin.
Login Audit records authentication activity, detects suspicious sign-ins, and applies configurable retention and IP-address handling.
Admins can filter and export login records, inspect recent activity, and receive alerts for configured suspicious-login conditions.
Status details:
- Status: Available
- Tier: premium
- Bundle: security-compliance
- Composer package:
capell-app/login-audit - Namespace:
Capell\LoginAudit - Theme key: not applicable
Why It Matters
Section titled “Why It Matters”For developers: Authentication events record exact audit rows; an after-commit observer delegates each created identity to focused detection and alert Actions. Privacy export, erasure, and retention also remain Action-owned.
For teams: Operators get an evidence trail for account access and a practical way to investigate unusual sign-in activity.
Screens And Workflow
Section titled “Screens And Workflow”Screenshot contract: docs/screenshots.json.
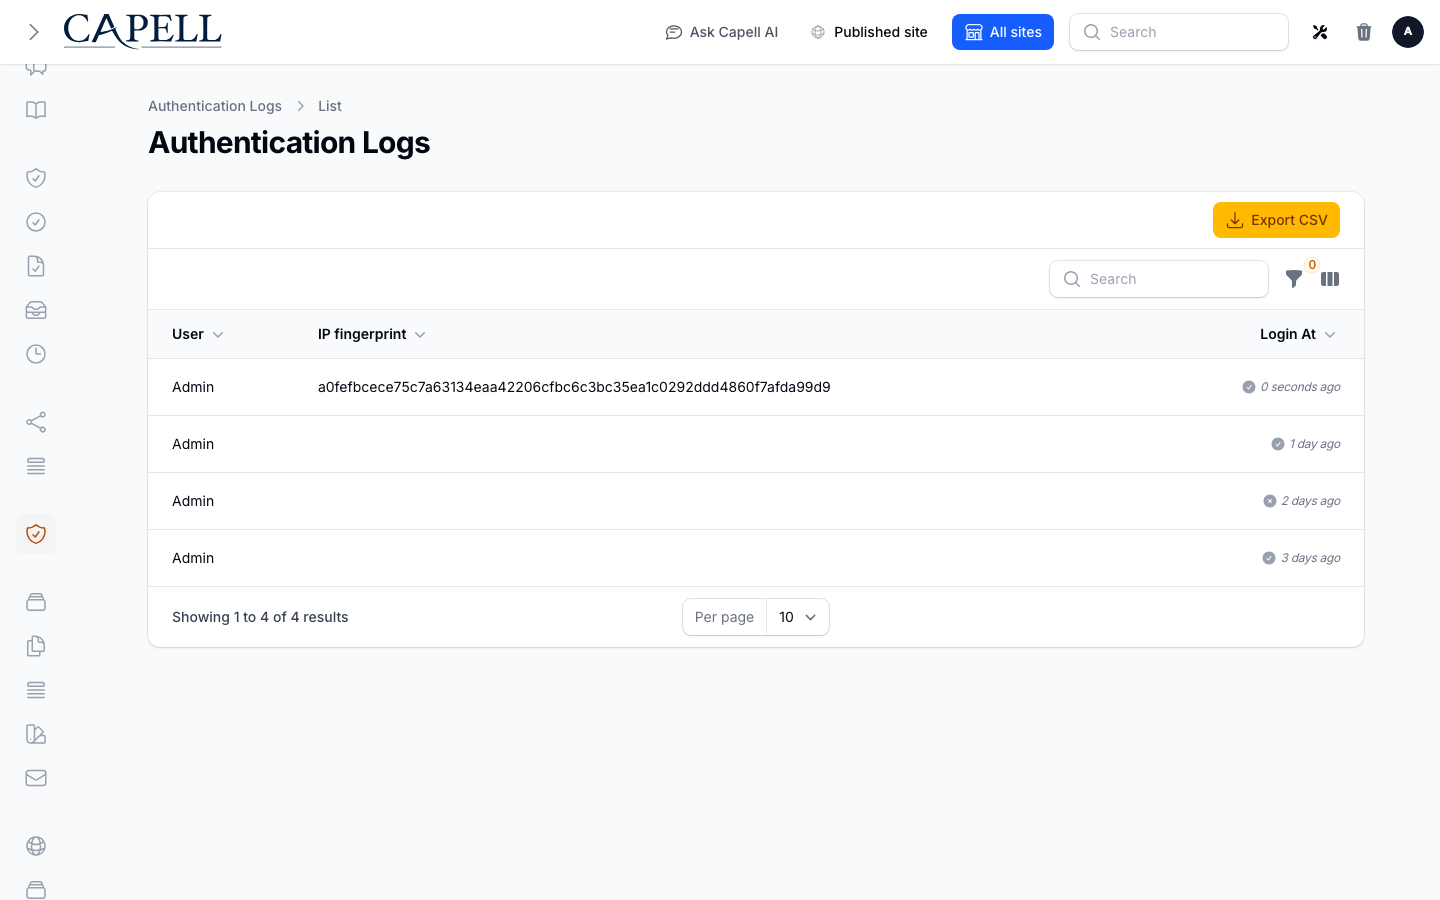
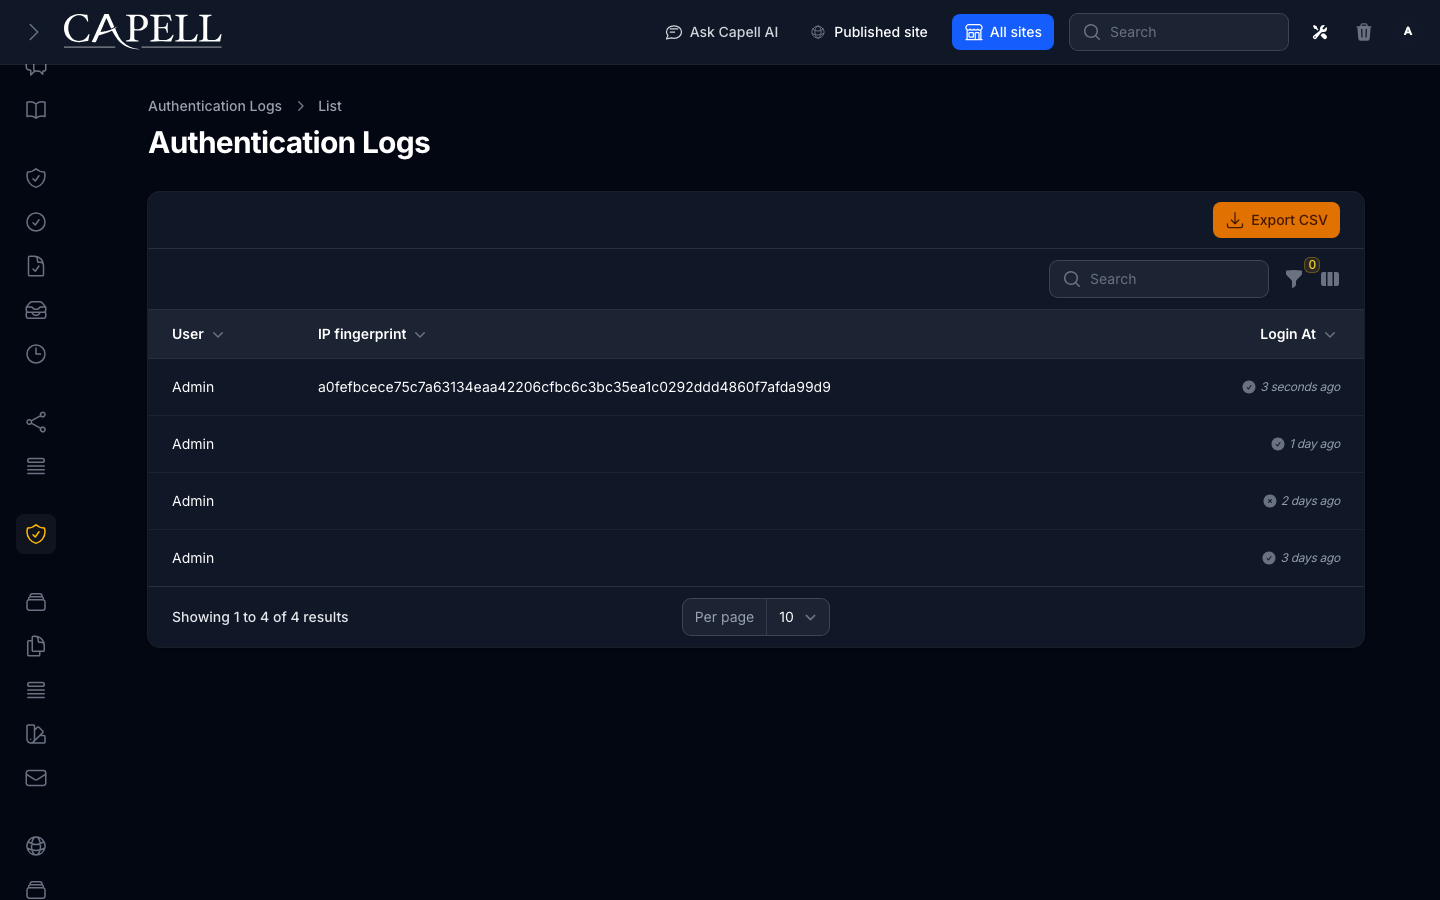
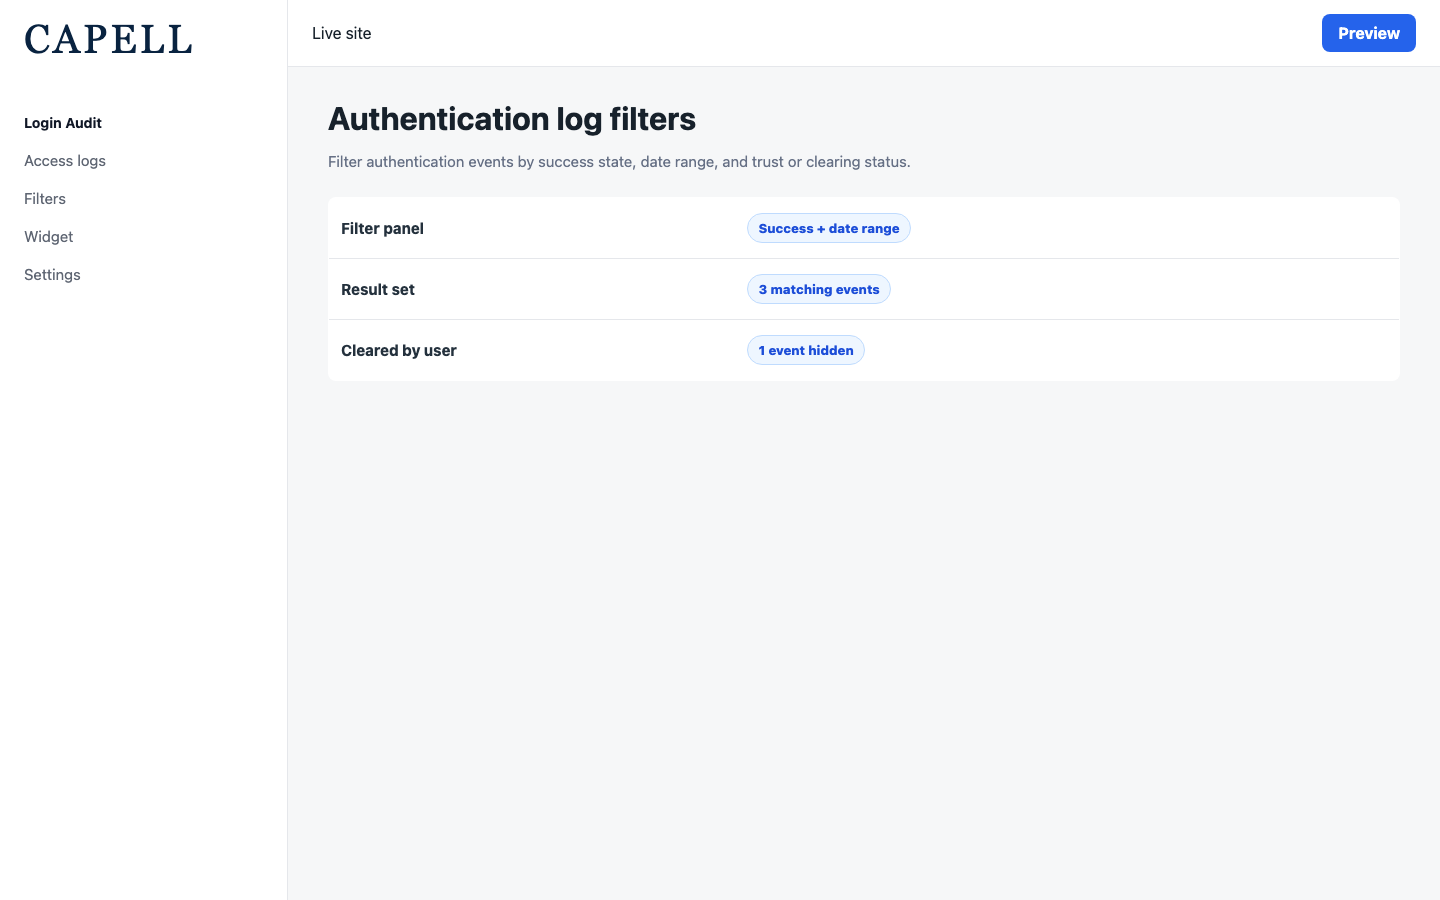
- Authentication logs admin index (admin, required authentic evidence).
- Authentication log table filters (admin, required evidence).
- Dashboard widget (admin, required evidence).
- Authentication log settings screen (admin, required evidence).
- User edit access summary (admin, required evidence).
- User authentication logs relation manager (admin, required evidence).
- Authentication logs admin index with admin sidebar menu open (admin, supplementary evidence).
Technical Shape
Section titled “Technical Shape”Service providers
Section titled “Service providers”Capell\LoginAudit\Providers\LoginAuditServiceProviderCapell\LoginAudit\Providers\AdminServiceProvider
Config files
Section titled “Config files”packages/login-audit/config/login-audit.php
Migrations
Section titled “Migrations”packages/login-audit/database/migrations/2026_05_10_190857_01_create_login_audit_table.phppackages/login-audit/database/migrations/2026_07_09_000001_add_activity_lookup_hashes_to_login_audit_table.phppackages/login-audit/database/migrations/2026_07_10_000001_drop_plaintext_ip_from_login_audit_table.phppackages/login-audit/database/migrations/2026_08_12_000001_repair_legacy_login_audit_schema.php
Settings migrations
Section titled “Settings migrations”packages/login-audit/database/settings/2026_05_10_190858_01_add_login_audit_settings.phppackages/login-audit/database/settings/2026_06_06_000001_add_login_audit_suspicious_detection_settings.phppackages/login-audit/database/settings/2026_06_06_000002_add_login_audit_alert_settings.phppackages/login-audit/database/settings/2026_06_06_000003_add_login_audit_geo_location_setting.phppackages/login-audit/database/settings/2026_08_05_000001_add_two_factor_reset_setting.php
Settings classes
Section titled “Settings classes”LoginAuditSettings
Models
Section titled “Models”LoginAudit
Filament classes
Section titled “Filament classes”LoginAuditAdminPanelExtenderLoginAuditResourceLoginAuditInfolistLoginAuditsTableLoginAuditsRelationManagerLoginAuditDashboardSettingsContributorLoginAuditSettingsSchemaLoginAuditsFilamentWidget
Policies
Section titled “Policies”LoginAuditPolicy
Listeners
Section titled “Listeners”LogoutListenerOtherDeviceLogoutListener
Actions
Section titled “Actions”ApplyLoginAuditSettingsActionBuildLoginAuditPrivacyExportActionBuildLoginAuditsCsvActionBuildLoginAuditsQueryActionDetectSuspiciousLoginActionEraseLoginAuditPrivacyDataActionProcessCreatedLoginAuditActionRecordLoginAuditPurgeActionResolveLoginAuditIpAddressActionSendLoginAuditAdminAlertActionShouldTrackAdminActivityActionShouldTrackUserIpAddressesActionUpdateLastSeenForActorAction
Data objects
Section titled “Data objects”LoginAuditEventDataLoginAuditRecordIdentityDataProcessedLoginAuditData
Manifest action API
Section titled “Manifest action API”applyLoginAuditSettings: Capell\LoginAudit\Actions\ApplyLoginAuditSettingsActionbuildLoginAuditsCsv: Capell\LoginAudit\Actions\BuildLoginAuditsCsvActionbuildLoginAuditsQuery: Capell\LoginAudit\Actions\BuildLoginAuditsQueryActiondetectSuspiciousLogin: Capell\LoginAudit\Actions\DetectSuspiciousLoginActionrecordLoginAuditPurge: Capell\LoginAudit\Actions\RecordLoginAuditPurgeActionresolveLoginAuditIpAddress: Capell\LoginAudit\Actions\ResolveLoginAuditIpAddressActionsendLoginAuditAdminAlert: Capell\LoginAudit\Actions\SendLoginAuditAdminAlertActionshouldTrackAdminActivity: Capell\LoginAudit\Actions\ShouldTrackAdminActivityActionshouldTrackUserIpAddresses: Capell\LoginAudit\Actions\ShouldTrackUserIpAddressesActionupdateLastSeenForActor: Capell\LoginAudit\Actions\UpdateLastSeenForActorAction
Scheduled commands
Section titled “Scheduled commands”authentication-log:purge (daily; package registered)
Manifest contributions
Section titled “Manifest contributions”admin-resource: Capell\LoginAudit\Manifest\LoginAuditAdminResourcesContributiondashboard-widget: Capell\LoginAudit\Manifest\LoginAuditDashboardFilamentWidgetContributionhealth-check: Capell\LoginAudit\Manifest\LoginAuditHealthContributionmodel: Capell\LoginAudit\Manifest\LoginAuditModelsContributionpermission: Capell\LoginAudit\Manifest\LoginAuditPermissionsContributionscheduled-job: Capell\LoginAudit\Manifest\LoginAuditPurgeScheduleContributionsetting: Capell\LoginAudit\Manifest\LoginAuditSettingsContribution
Health checks
Section titled “Health checks”Capell\LoginAudit\Health\LoginAuditHealthCheck
Data Model
Section titled “Data Model”- Required tables:
login_audit. - Models:
LoginAudit. - Migration files:
2026_05_10_190857_01_create_login_audit_table.php,2026_07_09_000001_add_activity_lookup_hashes_to_login_audit_table.php,2026_07_10_000001_drop_plaintext_ip_from_login_audit_table.php,2026_08_12_000001_repair_legacy_login_audit_schema.php. - Migration impact: run host migrations through the package install flow before opening package surfaces.
- Deletion/retention behaviour: retention is scheduled through
authentication-log:purge(daily; registered by the package provider).
Install Impact
Section titled “Install Impact”- Required packages:
capell-app/admin,capell-app/core. - Admin navigation: declares
admin-resource: LoginAuditAdminResourcesContribution; each Filament page or resource controls its own navigation visibility. - Admin/editor extensions:
dashboard-widget: LoginAuditDashboardFilamentWidgetContribution. - Permissions:
View:LoginAudit,Approve:TwoFactorReset; access also governed by package policies:LoginAuditPolicy. - Public routes: none declared.
- Database changes: package migrations are declared.
- Config:
config/login-audit.php. - Settings:
Capell\LoginAudit\Settings\LoginAuditSettings. - Queues or schedules: scheduled commands
authentication-log:purge (daily; package registered). - Cache tags: none declared.
- Commands: none declared.
Common Pitfalls
Section titled “Common Pitfalls”- Keep required Capell packages on compatible v4 releases:
capell-app/admin,capell-app/core. - Run migrations before opening package resources or public routes.
- Review package configuration before production-like verification:
config/login-audit.php,Capell\LoginAudit\Settings\LoginAuditSettings. - Keep the host Laravel scheduler running so package-registered schedules can execute:
authentication-log:purge (daily; package registered).
Troubleshooting
Section titled “Troubleshooting”| Symptom | Likely cause | Check | Fix |
|---|---|---|---|
| Package surface is missing after install | Provider or manifest is not loaded | Confirm capell.json, package composer.json, and provider registration | Reinstall the package, refresh Composer autoload, and clear host caches |
| Admin screen or command fails on missing table | Package migrations have not run | Check the tables listed in Data Model | Run host migrations and rerun the focused package test |
| Background work does not run | Queue worker or declared schedule is not active | Check the jobs and scheduled commands listed in Technical Shape | Start the queue worker or host scheduler, then run the focused command or package test |
Quick Start
Section titled “Quick Start”- Install the package:
composer require capell-app/login-audit. - Open the package admin surface at
/admin/login-audit/login-auditsand confirm Login Audit is available.
Next Steps
Section titled “Next Steps”- Package docs
- Overview
- Worked extension examples
- Admin guide
- Configuration files:
config/login-audit.php. - Troubleshooting
- Screenshot contract
- Marketplace assets
- Capell content language plan
- Capell documentation design system
- Capell and package ERD notes
- Related packages: Password Policy, Privacy Center, Diagnostics, Access Gate.